
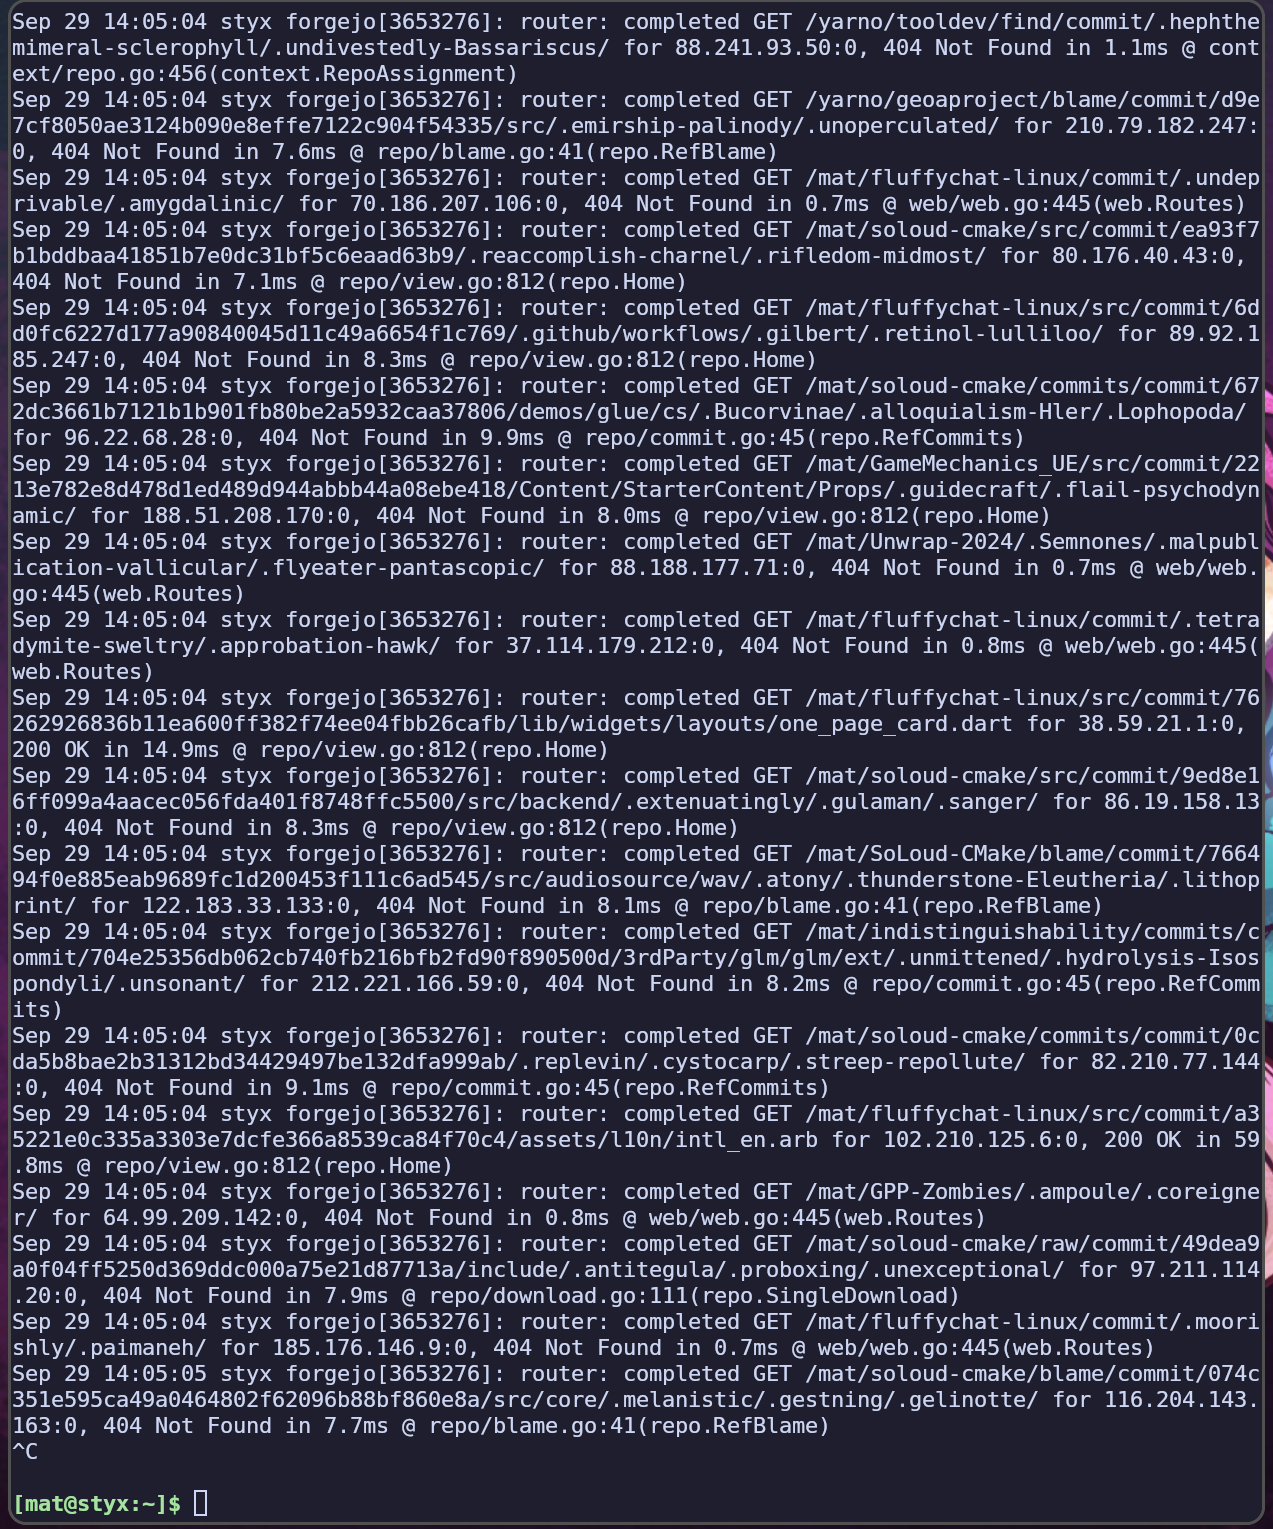
The AI DDoS is now targeting my Forgejo server with... a very strange attack. These are all getting past #iocaine. The ASNs appear to be quite diverse. What's going on?
0 Boosts
0 Likes


@allpurposemat
@maybe kindly ask @algernon for advice 🤔

@chfkch @allpurposemat I'd suggest enabling generated URLs. That should be the default with the built-in handler, with NSoE, you need to do it explicitly:
declare-handler nsoe {
checks {
generated-urls {
identifiers abrakadabra
}
}
}
Replace abrakadabra with a string that doesn't exist outside of the maze (you can have more than one listed there, and iocaine will choose one randomly).
That won't immediately fix the problem, but as soon as the crawlers start hitting the generated URLs, they'll be trapped.
Then, you can enable the firewall to reduce the amount of garbage iocaine serves.
These things get through, btw, because they're either real remote chromes, or (less likely) emulate them at sufficient level to be hard to distinguish.
Meanwhile, what you can try, is also enabling the Cookie Monster (if using Nam-Shub of Enki):
declare-handler nsoe {
checks {
cookie-monster {
forgejo-hosts forge.example
}
}
}
That'll put up a small cookie wall that I found a lot of these chromes won't pass.
Hope that helps! If not, let me know, and I'll try to figure something else out.

oh lol, those are the iocaine URLs. Some crawler started getting thru iocaine, but still requesting its URLs.
Maybe I can set something up to auto-ban IPs that fetch these? nginx stuff is way past me, but good chance to learn I guess.
Also would be nice to ratelimit #iocaine, as it's exhausting nginx's resources by serving so much poison. Seems to be unsupported (for now) though without affecting Forgejo itself: https://git.madhouse-project.org/iocaine/iocaine/issues/159#issuecomment-4219
Cookie monster!